Most products have a privacy policy.
Fewer have actually mapped their data flows,
locked down consent, and documented what happens
when a user asks to be forgotten.

GDPR compliance
beyond the checkbox

Book an audit

Where most implementations
fall short

Having a privacy policy and a cookie banner covers the visible layer.
The gaps that create real exposure are underneath —
in data flows, consent records, and features nobody thought to audit.

Cookie consent that doesn't hold up

Cookie consent that doesn't hold up

A banner that looks compliant often isn't. Consent needs to be granular, recorded, and revocable — and what's implemented needs to match what's actually firing on the page.

Data flows nobody has mapped

Data flows nobody has mapped

GDPR requires knowing what personal data you collect, where it goes, and who processes it. Across APIs, analytics tools, and third-party services, that picture is rarely documented.

Rights requests with no working backend

Rights requests with no working backend

If your product can't reliably fulfill a deletion or access request, that's a compliance gap — regardless of what the privacy policy says.

Enforcement isn't only for big companies

Enforcement isn't only for big companies

The pattern in regulatory actions is consistent: not malicious intent, but incomplete implementation and missing documentation.

What the compliance
work covers

GDPR compliance isn't a single deliverable.
We work through the technical layer systematically — from data mapping
to consent implementation to documentation.

icon

Data mapping & ROPA

We document what data your product collects, where it flows, and who processes it.

icon

Consent management

Consent implementation with granular categories, proper records, and a working opt-out.

icon

Data subject rights

Technical implementation of access, deletion, and portability — no manual workarounds.

icon

Privacy by design review

Storage, retention, and data architecture reviewed against what your privacy policy claims.

icon

Third-party & processor audit

Every external service touching personal data checked for DPAs and transfer compliance.

How the engagement
works

01 — Map the current state

icon

What your product actually does with personal data — not what the policy says, but what's in the system.

02 — Identify the gaps

icon

Data flows, consent logic, third-party processors, and rights-handling reviewed against GDPR requirements.

03 — Implement the fixes

icon

Consent setup, data subject rights flows, retention policies, DPA documentation. Legal language stays with your counsel.

04 — Document & hand off

icon

Completed ROPA, updated privacy documentation, and an audit-ready record of what was done.

icon
Vilmate
Not sure where your gaps are?
Talk to our team — we'll tell you what's likely in scope and what isn't
before any work begins.
Talk to our team

Why Vilmate

Your Team, Not a Rotation
Speed Without Shortcuts
ISO-Certified Quality
Nearshore Advantage
image
You work with the same developers start to finish. No handoffs, no "let me check with the team", no lost context mid-project.
image
We move fast — but not at the expense of code quality or architecture. Fast and clean aren't mutually exclusive.
image
Our processes are ISO-certified. That means structured code reviews, clear documentation, and predictable delivery.
image
Based in Eastern Europe, we overlap with US and EU working hours. Real-time collaboration without the timezone headache.

Selected work

A few projects that started with a challenge and ended with something that works.

See all cases
BigCommerce Store Optimization
#e-commerce
#aws
#bigcommerce
#contentful
#graphql
#next.js
#node.js
#react
USA

BigCommerce Store Optimization

Global outdoor apparel brand
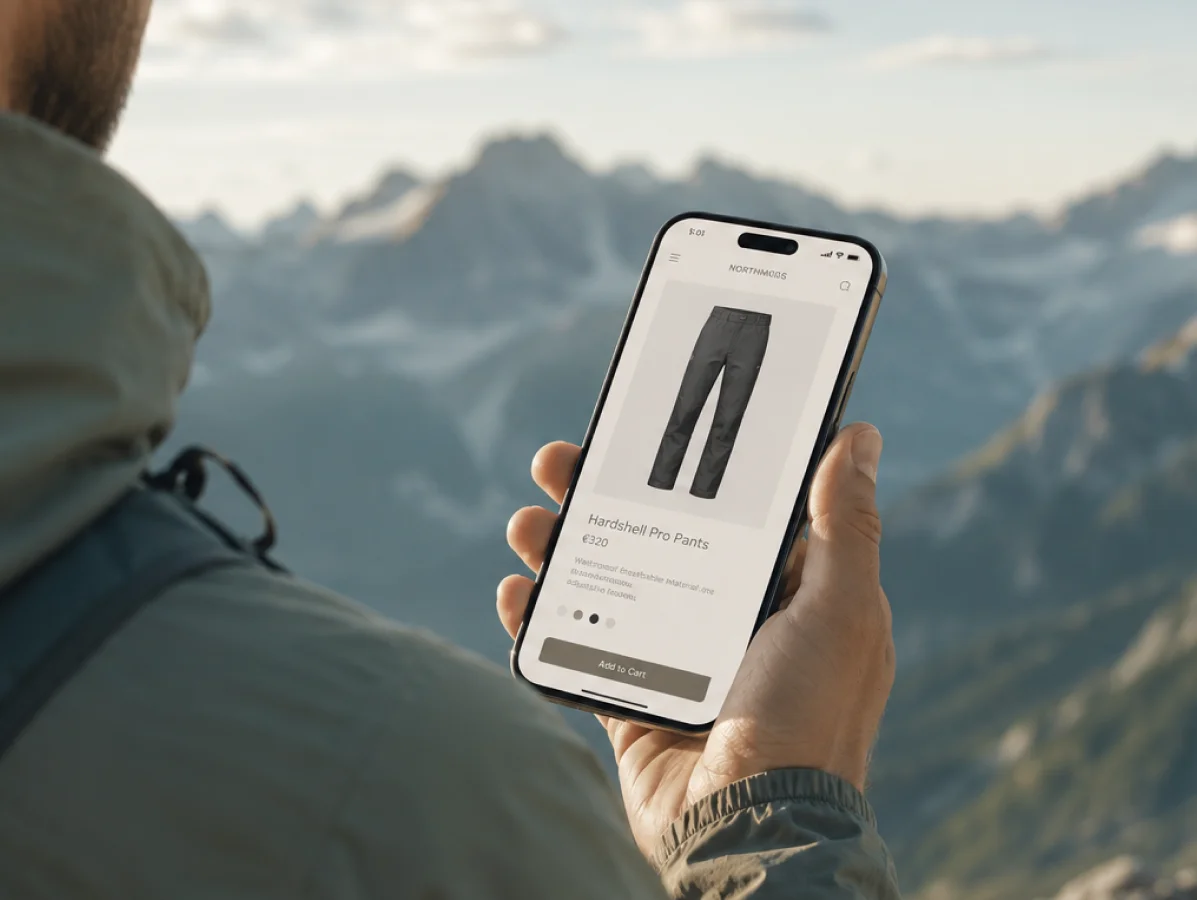
A technical audit led to long-term work on the BigCommerce store. Our development team took technical ownership, reworking its architecture, integrations, storefront UX, and release process.
80%
Codebase Refactored
90%
Backend Features Rewritten
2×
Lower AWS Costs
View case study
SFCC Store Stabilization and Enhancement
#e-commerce
#.net
#node.js
#sfcc
#wordpress
USA

SFCC Store Stabilization and Enhancement

Platform enhancement for a leading US retail and entertainment company
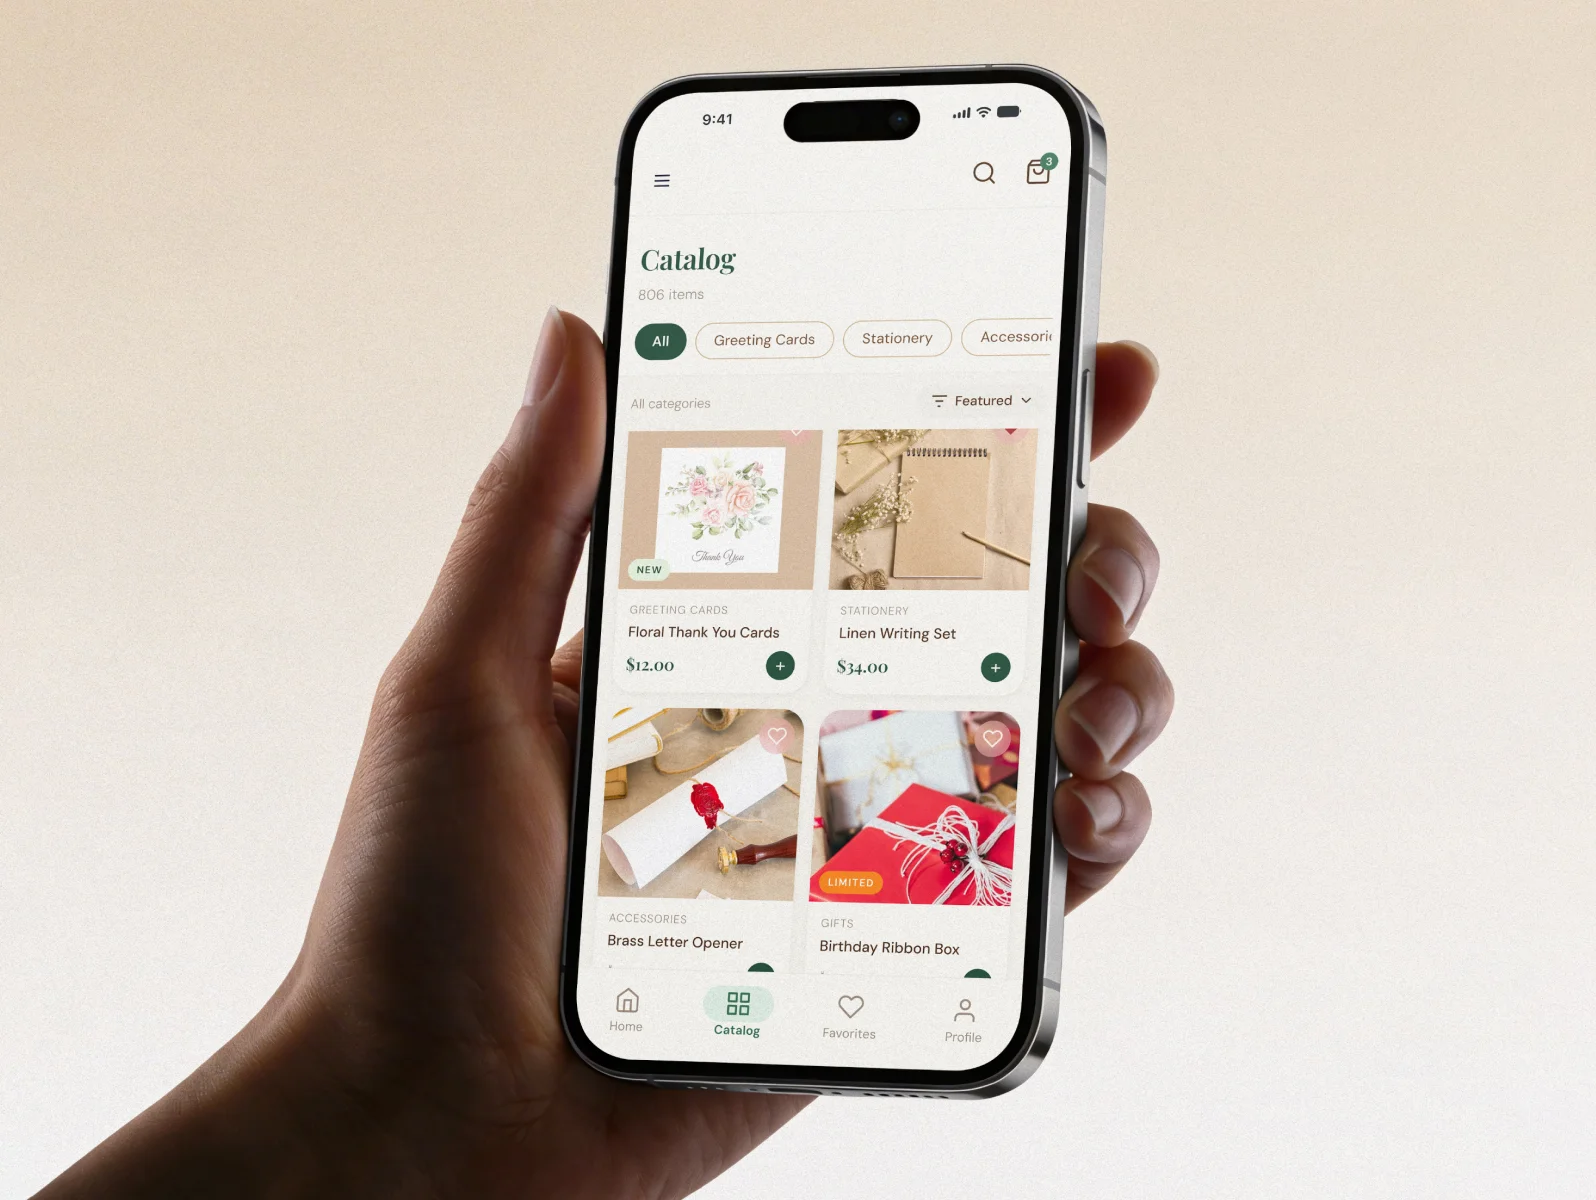
A century-old greeting card brand needed more than a quick fix. We stabilized their SFCC platform, built QA automation from scratch, and brought consistency to their mobile apps.
View case study
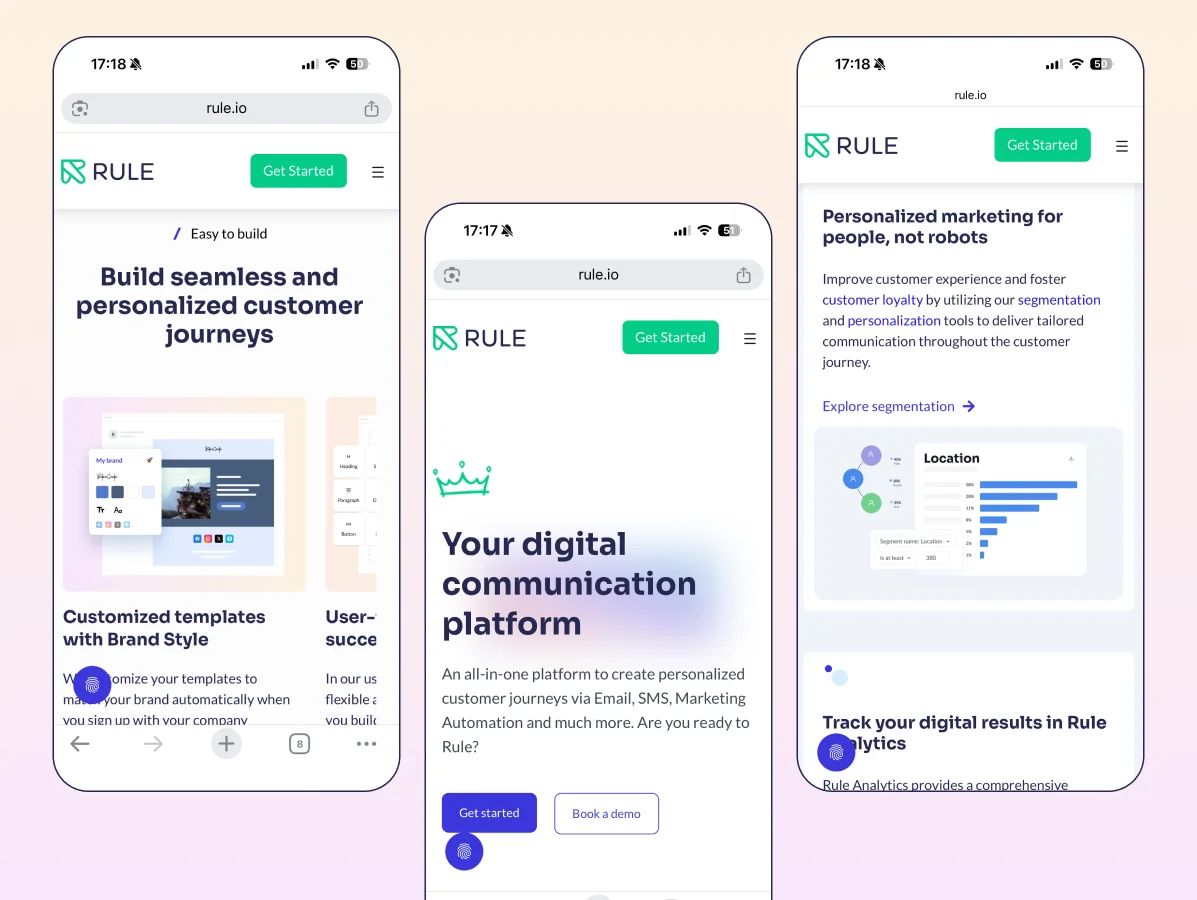
Rule
#adtech
#angular
#laravel
Sweden

Rule

Marketing automation platform for email and SMS campaigns
RuleMailer was already in use, with key functionality still to add. Our development team worked on the Template Editor, external integrations, subscriber communication, and campaign statistics.
2×
Development Speed
~50% lower
Development Costs
Stable
Under Growing Demand
View case study

Questions clients ask
before they start

Do you provide legal advice as part of this?
No — and that's intentional. We handle the technical implementation: data mapping, consent management, rights flows, and architecture review. Legal interpretation stays with your counsel. The two work better together than either does alone.
Our product already has a cookie banner. Do we still need this?
Probably. A banner handles the visible layer, but GDPR compliance runs deeper — consent records, data subject rights, processor agreements, retention policies. Most banners don't cover those.
We're a US company but have EU users. Does GDPR apply to us?
Yes. GDPR applies based on where your users are, not where your company is incorporated. If you're processing personal data of EU residents, you're in scope.
How long does a compliance engagement take?
Depends on the product complexity. A focused audit with remediation typically runs four to eight weeks. We'll give you a realistic estimate after the initial scoping call.
What do we get at the end?
A completed ROPA, documented data flows, implemented technical fixes, and a clear record of what was done — enough to demonstrate compliance if a regulator or client asks.

Let's look at
what needs fixing.

Share what you're working with and we'll put together a scoping proposal.
Prefer a call?
Pick a time that works for you.
Book a call


    Latest insights

    Who Should Build Your AI System, and Why Consider a Forward Deployed Engineer?
    October 28, 2026
    Anastasiia Rezinkina
    Who Should Build Your AI System, and Why Consider a Forward Deployed Engineer? #AI & ML
    If you’ve already worked out where AI makes sense in retail, what implementation challenges can arise, and what defines AI readiness of your e-commerce stack, one decision remains: who is going to build it? That question is one reason a forward deployed engineer keeps coming up in AI conversations. The role puts an engineer directly […]
    AI Readiness Assessment for Teams That Have Already Said Yes to AI
    October 21, 2026
    Anastasiia Rezinkina
    AI Readiness Assessment for Teams That Have Already Said Yes to AI #AI & ML
    Ask an e-commerce team if they’re ready for AI and there’s a good chance the answer will be an immediate “absolutely.” And they probably mean it. Competitors are already using AI, plenty of everyday work could use automation, and there are usually a few ideas the team would happily start tomorrow. The answer gets less […]
    AI in Retail: Where Does It Actually Pay Off?
    October 14, 2026
    Anastasiia Rezinkina
    AI in Retail: Where Does It Actually Pay Off? #AI & ML
    If AI has suddenly become one more thing your retail team is expected to figure out, we get it. There are vendor demos, competitor launches, internal questions, and probably a few very confident opinions about what you should be doing already. That can make AI in retail feel like a decision you’re late to. You’re […]